The practice grew past the point where a shared password vault per technician was safe. Pam Terminal gave them tenant-aware strategies, recording, and clean offboarding.
“Technicians see only the tenants they are staffed on. When a client leaves, we revoke a strategy — not chase secrets across laptops.”
Needs
Cross-tenant credential reuse created unacceptable blast radius if a laptop was lost.
Clients increasingly asked for session recordings as part of the MSA.
Scheduling technicians across tenants required fast grant/revoke without reimaging machines.
How the Team Uses Pam Terminal
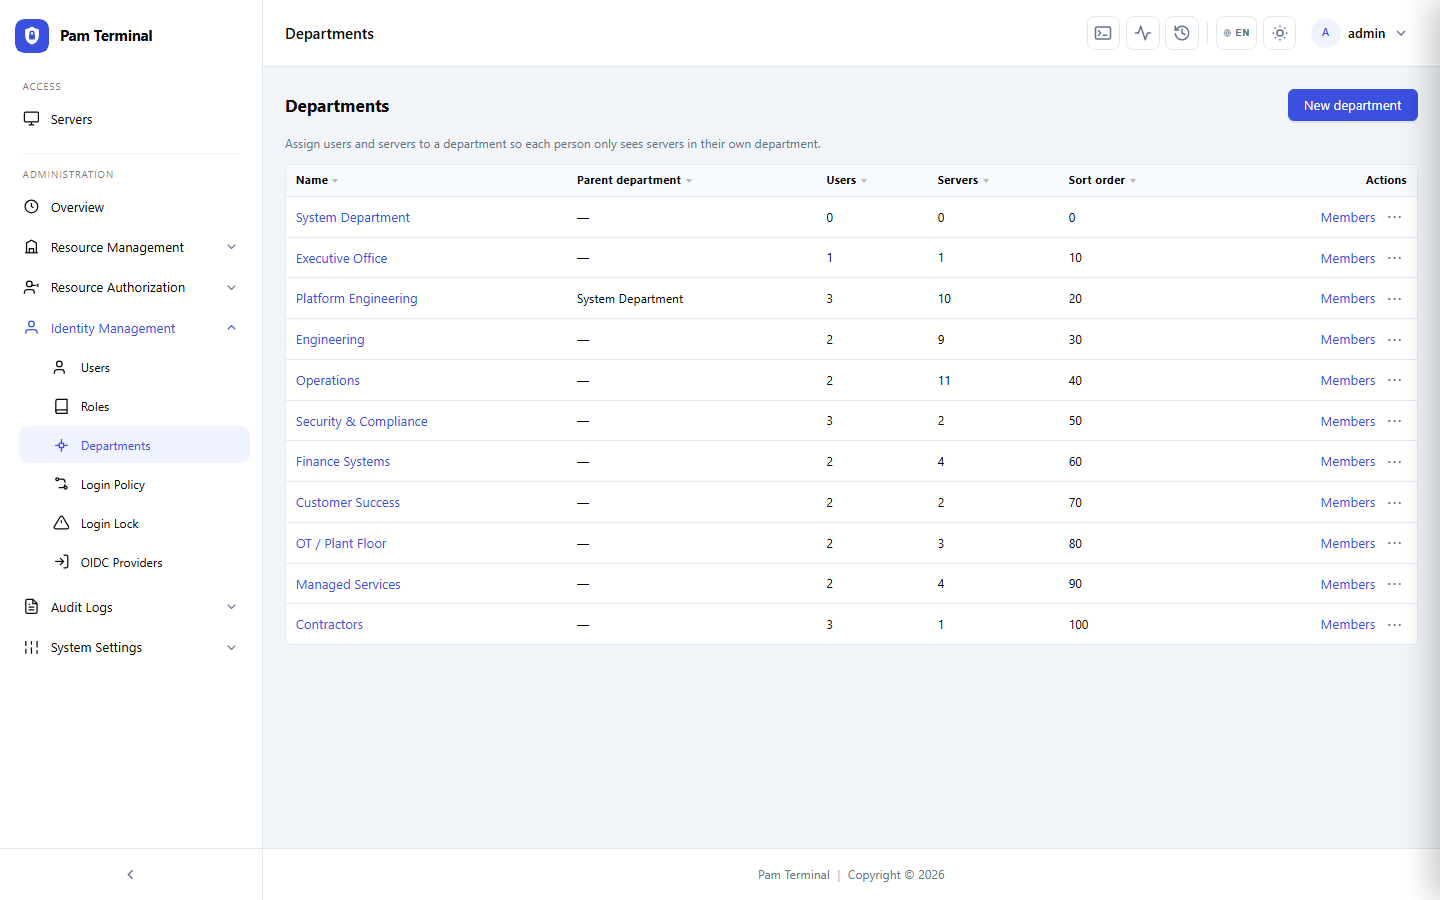
Each client is a Pam Terminal group with its own assets and strategies. Technicians inherit access from staffing roles.
“Recording every tenant session is now a sales advantage — buyers understand we can prove isolation.”
Night-shift coverage uses the same browser gateway from approved offices and remote locations.
Results
Service delivery metrics after Pam Terminal became the only privileged path.
35+
Client Tenants Segregated
0
Cross-Tenant Credential Reuse
2X
Technician Throughput
100%
Client Sessions Recorded
10m
Avg Time to Staff a New Tenant
1
Privileged Access Control Plane