The SOC needed to prove who did what on production hosts. Pam Terminal’s session recording and audit events replaced incomplete command histories.
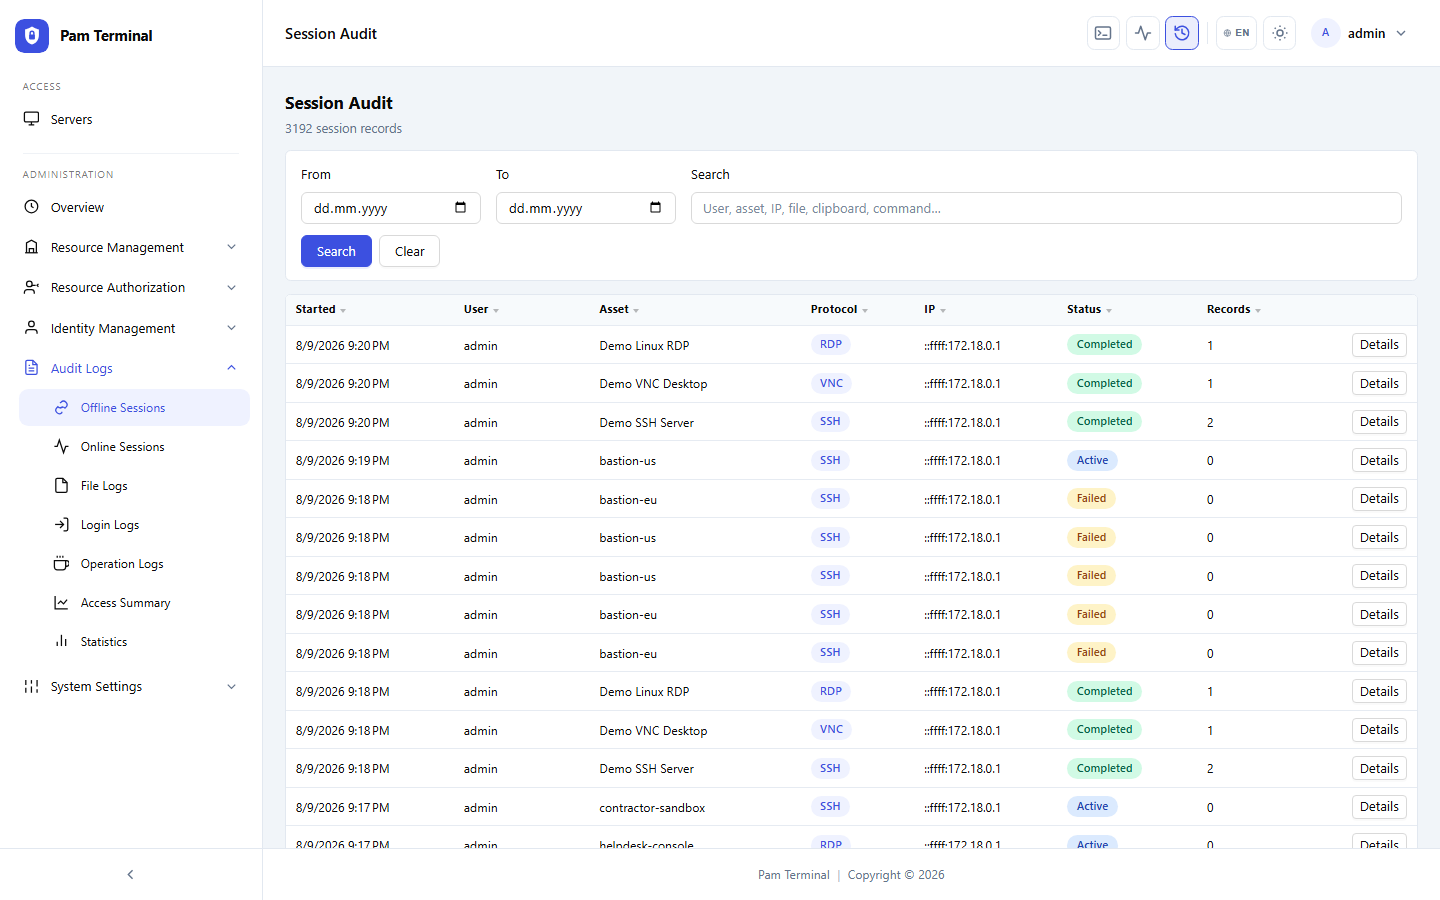
“Auditors ask for samples; we send Pam Terminal replays with identity, timestamp, and asset. That conversation used to take a week of log stitching.”
Needs
Command logging alone missed GUI actions on RDP jump boxes and clipboard transfers.
External auditors rejected screenshots as insufficient evidence of continuous monitoring.
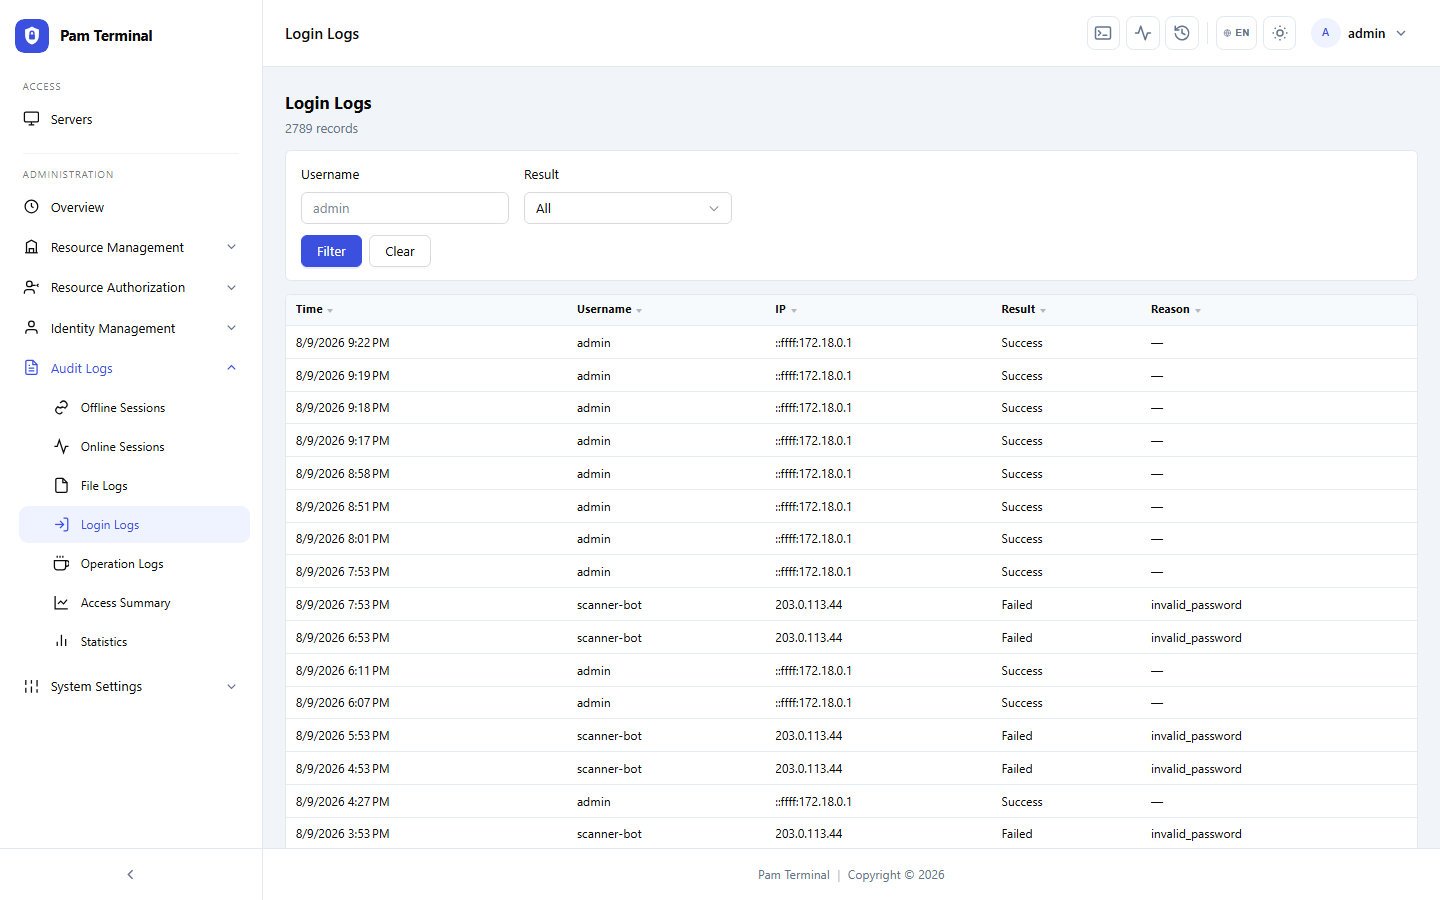
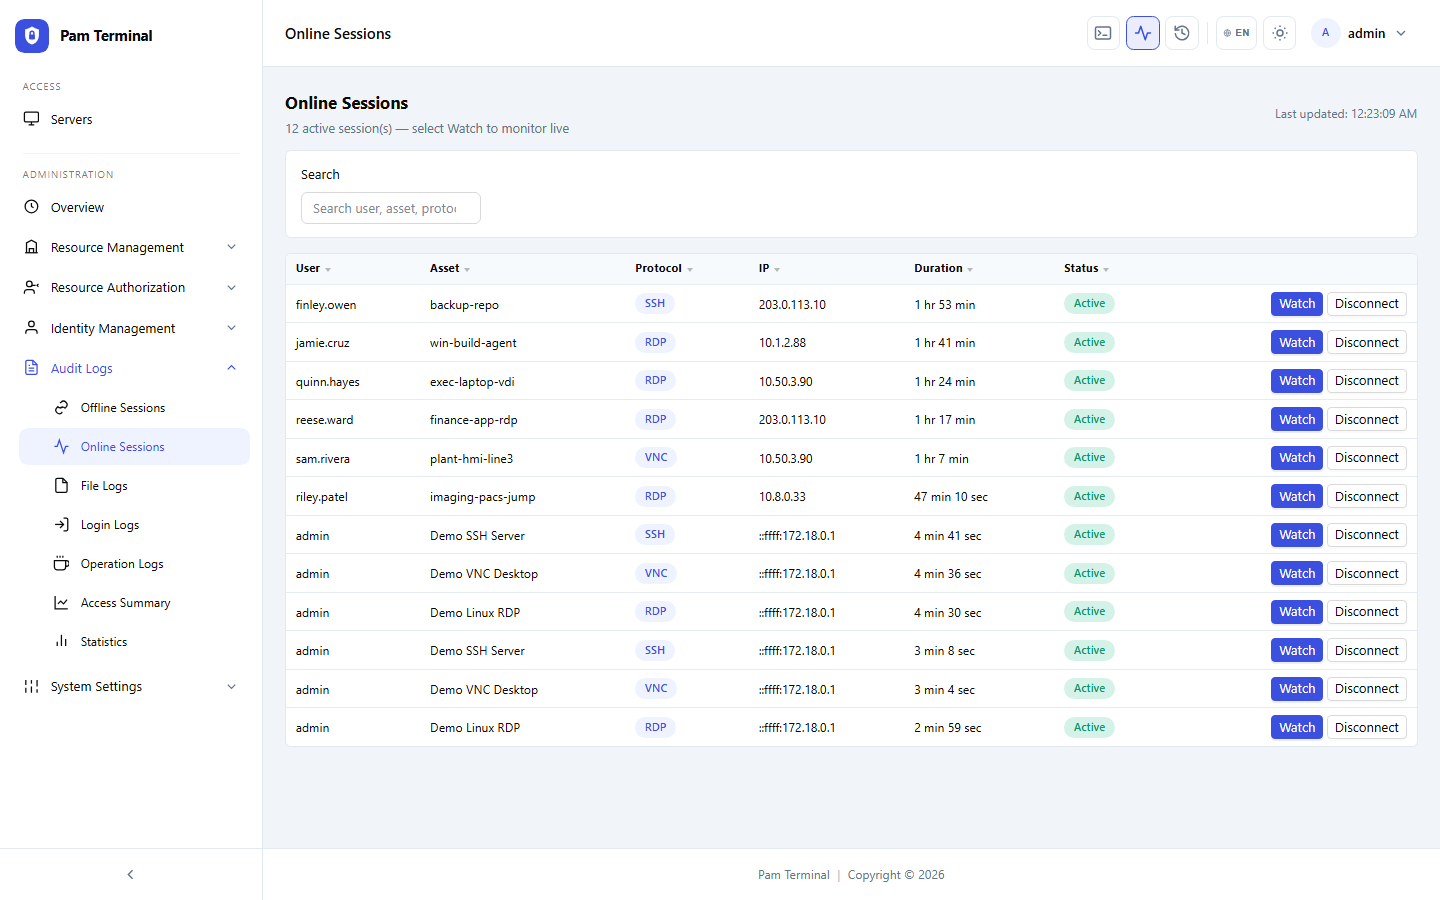
The SOC wanted live watch and terminate for suspicious privileged sessions.
How the Team Uses Pam Terminal
Every production SSH/RDP path terminates in Pam Terminal. Watermarking and recording are mandatory policy.
“Live monitoring means we can coach an engineer mid-session or cut access if scope drifts.”
Quarterly access reviews export Pam Terminal strategies and session inventories as evidence packs.
Results
What the SOC measured after enabling Pam Terminal recording everywhere.
100%
Privileged Sessions Replayable
70%
Faster Audit Sampling
0
Unattributed Prod Shells
12m
Session Retention Window
4m
Avg Time to Pull Evidence Clip
99%
Sessions Mapped to IdP Users